[Tech and AI partner]

Raise the level of security across your applications and infrastructure

We audit your code and infrastructure, test your defences under real-world conditions, then hand you a prioritised remediation plan, with the time needed for each fix.
Your vulnerabilities fixed, confirmed by a follow-up audit report
150+ security audits and penetration tests carried out
5 application security engineers, backed by 140+ senior tech specialists
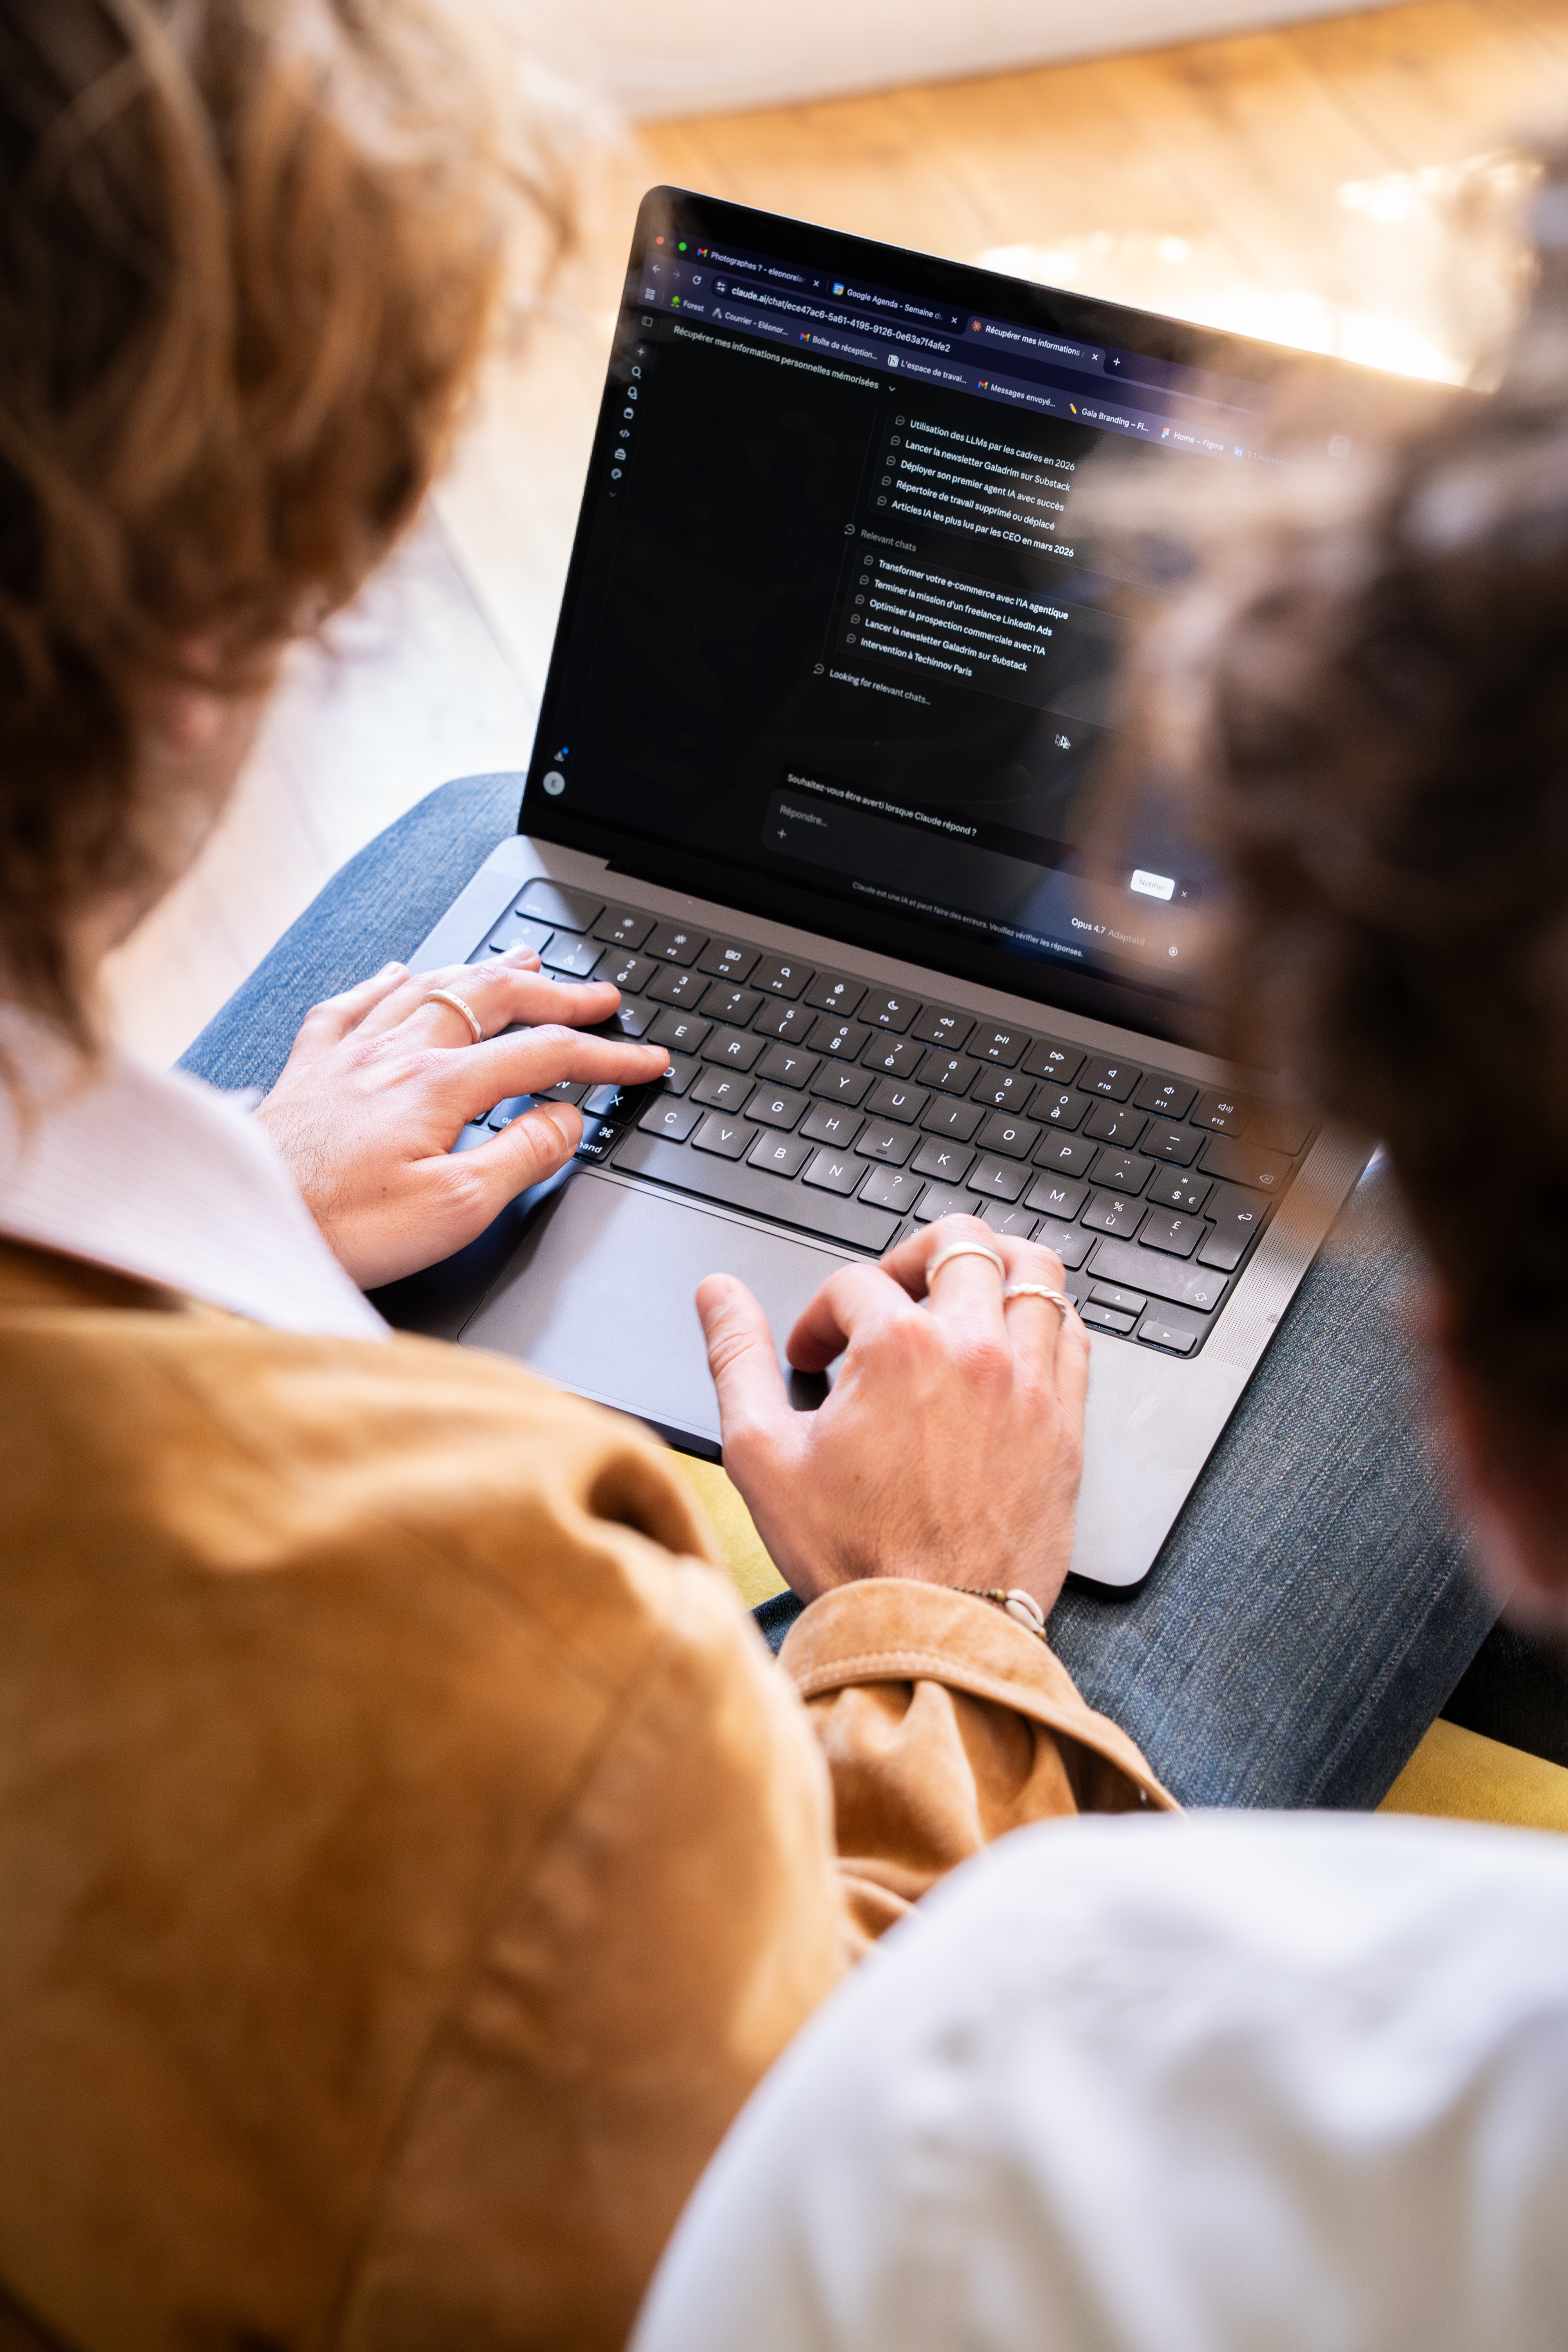
Two Galadrim consultants reviewing work on a laptop
800+ organisations trust us with their tech and AI projects
Two Galadrim engineers doing a code review
Code, cloud configurations and attack methods change all the time, and even the most carefully built applications end up with blind spots. To keep raising your level of security, it isn't enough to have an outside eye find your vulnerabilities. You need concrete, prioritised ways to fix them.
Robin BaraudHead of Cybersecurity
[What we offer]

We measure how secure your applications and infrastructure really are, then fix the flaws and confirm they're gone.

Application security audit

Application security audit

We analyse your code and its configuration: authentication, access rights, data exposure, secrets and dependencies. With or without access to the source code — your choice.
Penetration testing

Penetration testing

A controlled attack on your web application, APIs, mobile app or network, within a scope agreed with you. Every vulnerability we exploit comes with proof of impact.
Cloud infrastructure audit

Cloud infrastructure audit

A review of the architecture and configuration of your cloud environments. It covers identities, network segmentation, encryption and hardening, against the CIS Benchmarks.
Remediation and follow-up audit

Remediation and follow-up audit

Your teams or ours fix the flaws. A follow-up audit then checks they're gone and confirms it in writing.
Continuous protection and incident response

Continuous protection and incident response

A web application firewall run by our teams, with regular reports on your exposure.
[How we work]

Our method for measuring and fixing your vulnerabilities

  • Scoping
    Step 01

    Scoping

    We agree the scope, access method and timeline with you before anything is signed.
  • Audit
    Step 02

    Code audit and penetration test

    We run both in parallel, with auditors from outside the teams that built the application, and report vulnerabilities to you as we find them.
  • Reports
    Step 03

    Audit reports

    We describe each vulnerability, rate it using the CVSS standard and give an estimated time to fix it.
  • Debrief
    Step 04

    Debrief

    We present our findings to your technical teams and management in a debrief session. Then we turn the report into a compliance roadmap aligned with the recommendations of ANSSI, France's national cybersecurity agency.
  • Remediation
    Step 05

    Remediation and follow-up audit

    Your teams or ours fix the flaws, then a follow-up audit checks they're gone and confirms it in a report.
01/05
[Our team]

Application security engineers, backed by Galadrim's technical teams

Robin Baraud
Robin Baraud Partner and Head of Cybersecurity
A former solutions architect trained in low-level programming and cybersecurity, he leads Galadrim's security offering, scopes each engagement as lead auditor and reviews every report before it goes out.
Benjamin Drighès
Benjamin Drighès Partner and CTO Data & AI
A former adviser at the Autorité des marchés financiers, the French financial markets regulator, he chairs Galadrim's security committee. He runs the code audit campaigns on our AI projects, all the way to verifying that every critical flaw has been fixed.
Surya Ambrose
Surya Ambrose Head of Engineering
Engineering Manager for four and a half years at a fintech regulated by France's AMF, he sets Galadrim's engineering standards and oversees our teams' access to client environments.
Baptiste Vilboux
Baptiste Vilboux Lead Developer
He is leading Galadrim's ISO 27001 certification process, having spent more than a year modernising the legacy software of a group of 900 pharmacies without interrupting operations.
Julien Schmitt
Julien Schmitt AI Engineer
A member of Galadrim's security committee, he works on secrets and access management across our projects.
[Our work]

They trusted us with the cybersecurity of their most sensitive software

Wealth managementPraemia REIM

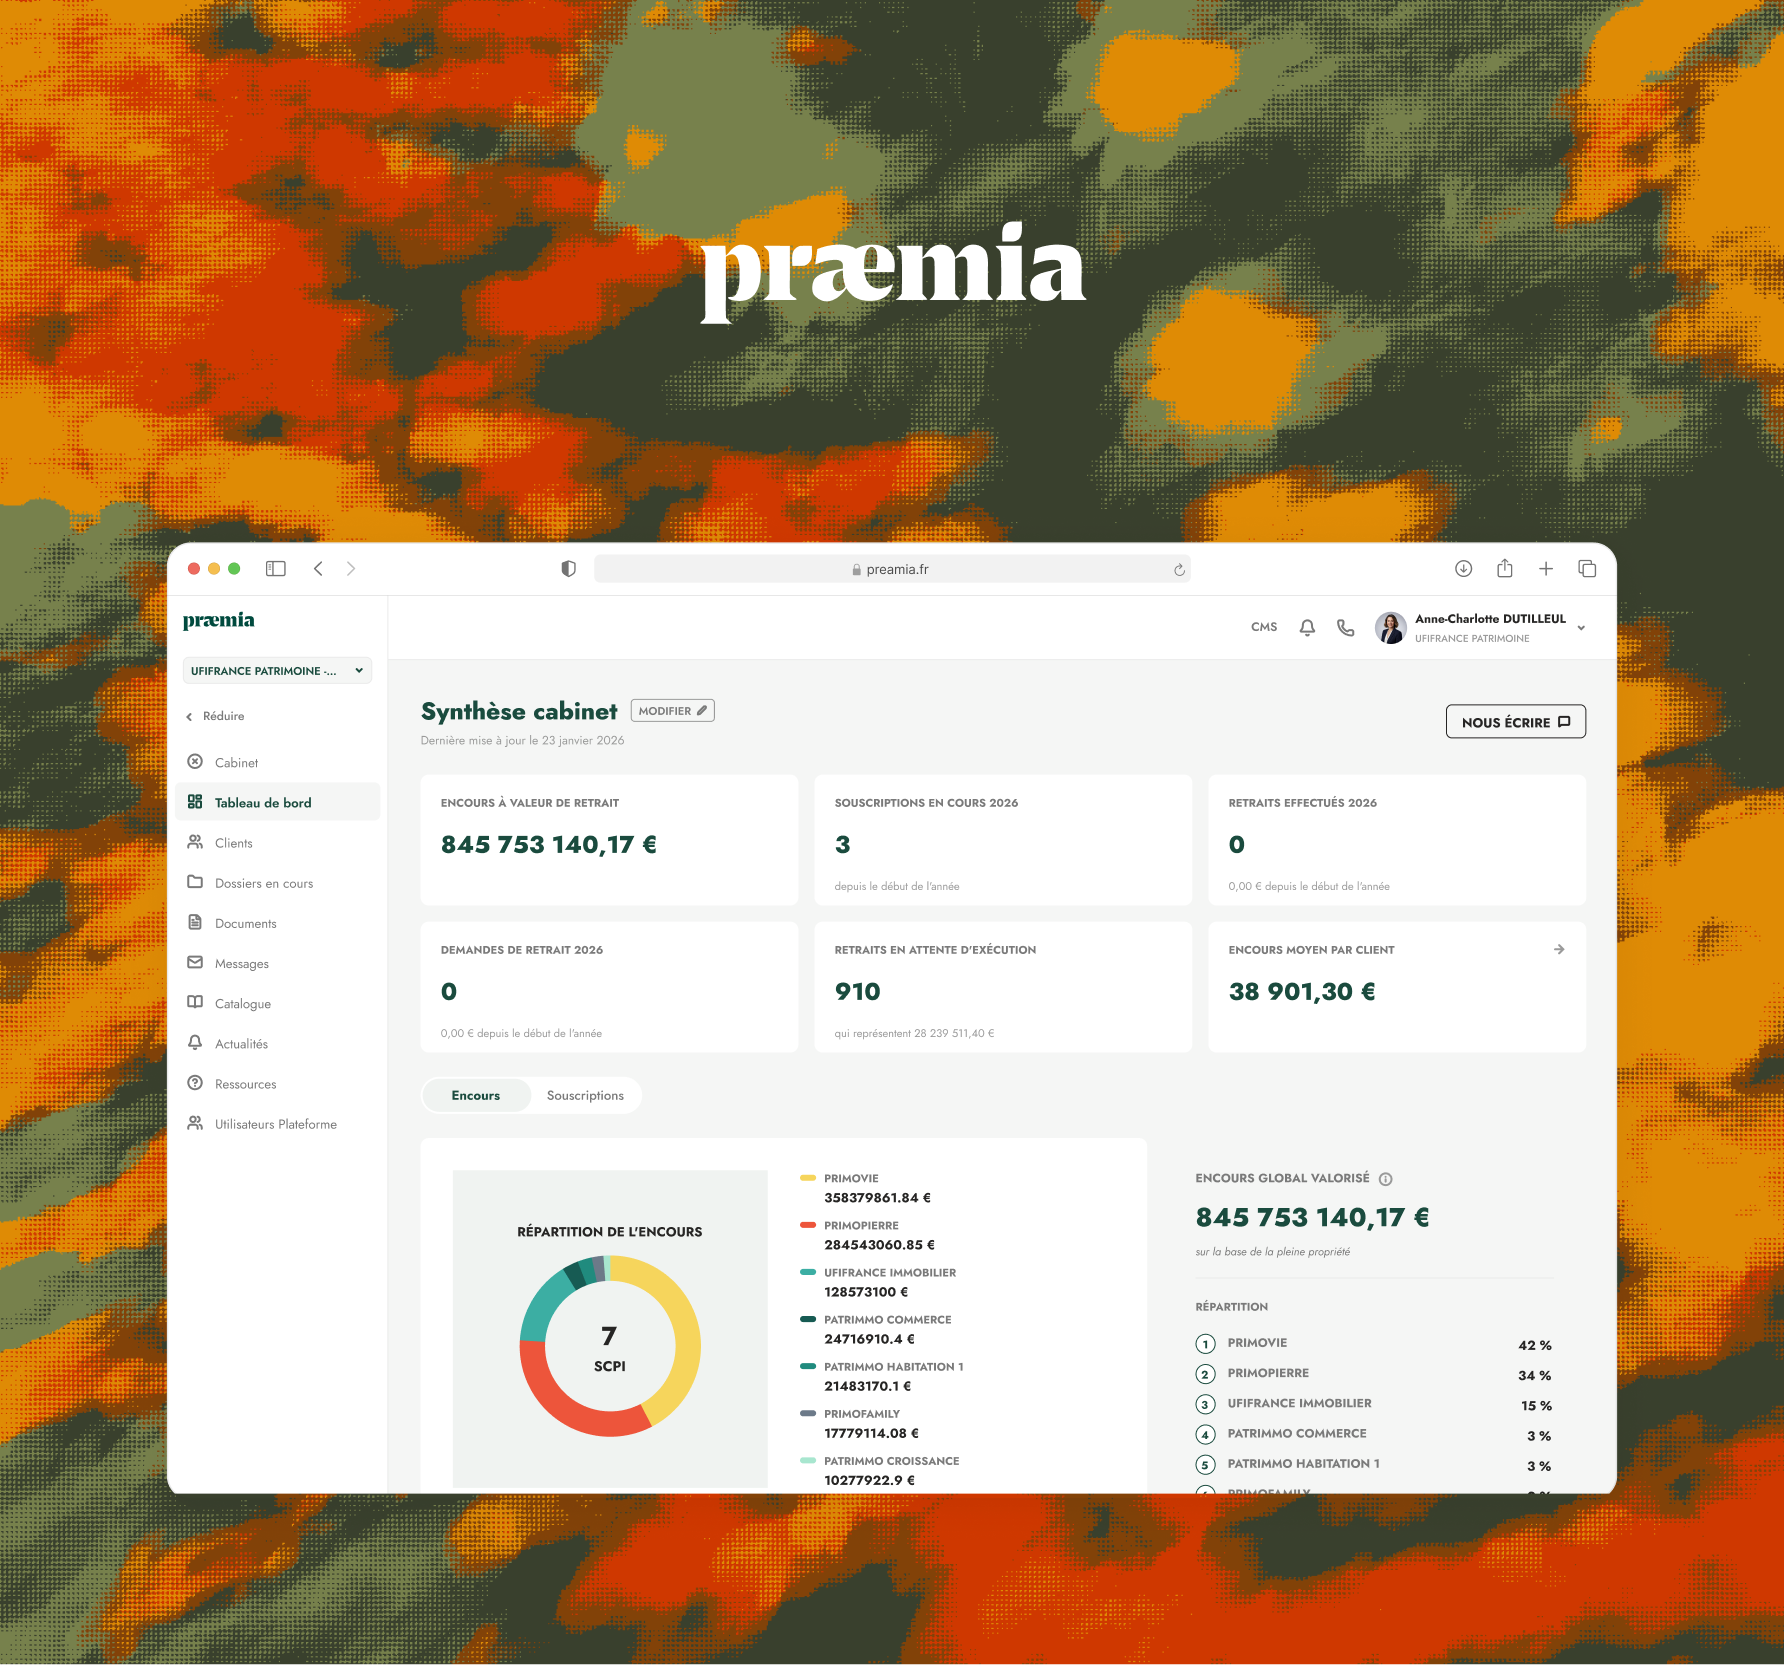
Getting an independent pentest to validate the extranet of a €33bn asset manager

Praemia REIM gives independent wealth advisers a view of the full lifecycle of their clients' SCPI investments (French real estate investment funds): assets under management, subscriptions, tax and commissions. Galadrim designed and built this extranet: multi-strategy authentication including enterprise single sign-on, server-side permissions, encrypted secrets in the deployment pipeline and four isolated environments. The client commissioned a specialist firm to run a penetration test and then a follow-up audit, which both awarded the highest security rating on its assessment scale.
€33bnin assets under management
61funds tracked
Highest ratingin the third-party follow-up audit
Praemia REIM Logo
TelecommunicationsIliad

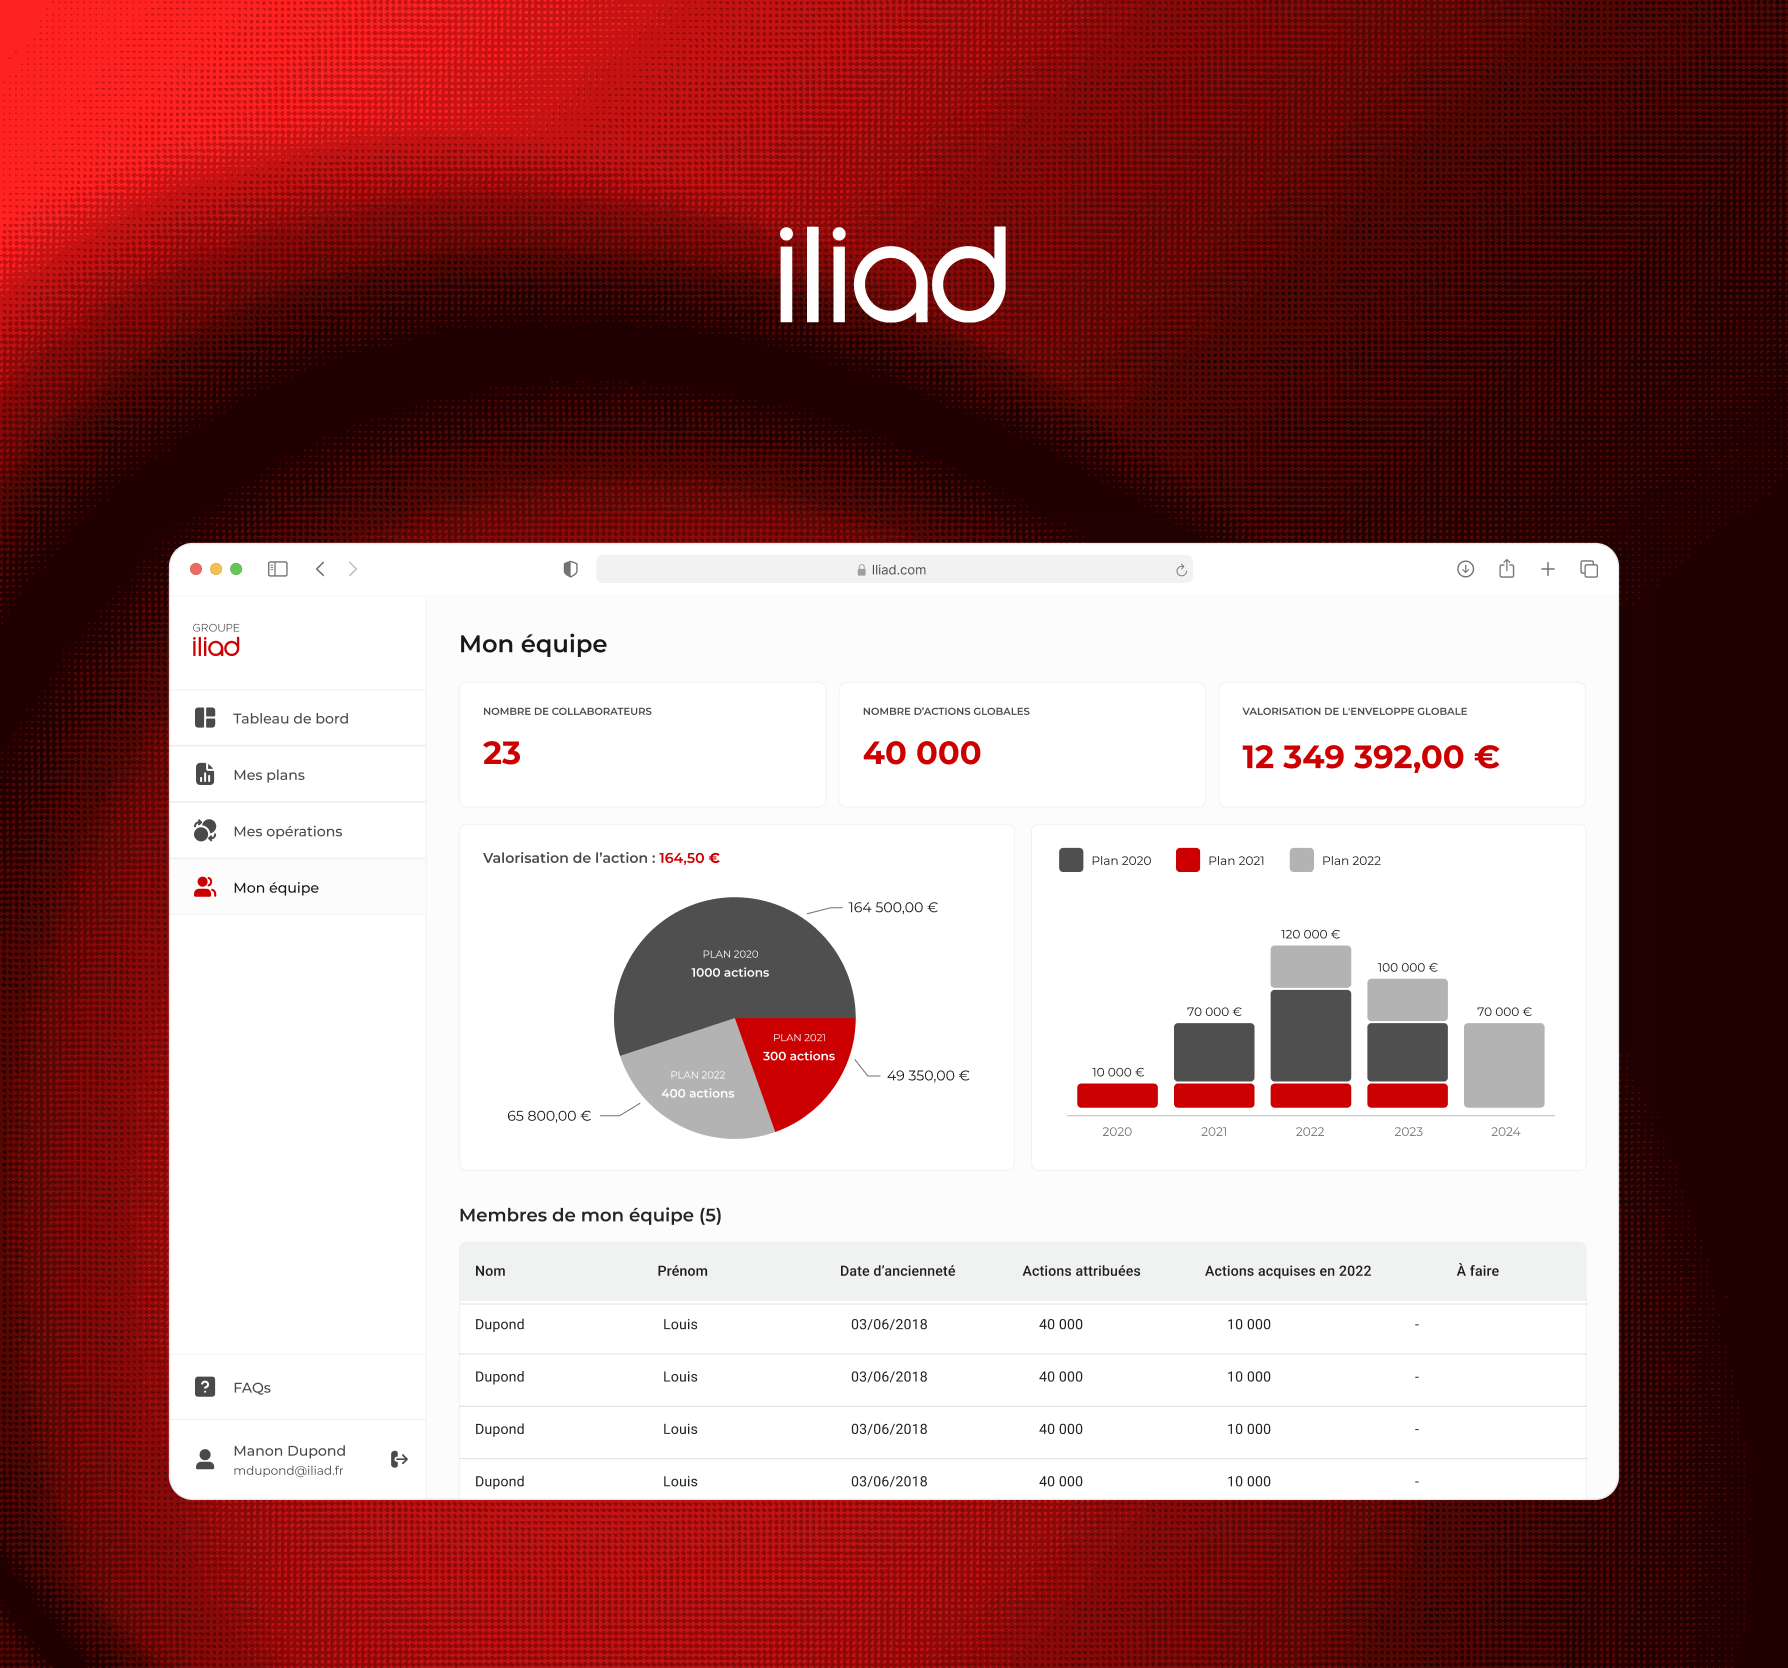
Showing 12,000 employees their pay and free shares under strict access control

Iliad, owner of the telecoms operator Free, wanted to give every employee a view of their total pay, benefits cover and free share plan. Galadrim built the two applications on a fine-grained role model that determines what each employee, manager and administrator can see. Legal documents for share transfers go through the platform.
12 000users
1M+rows of data
2separate applications
Iliad Logo
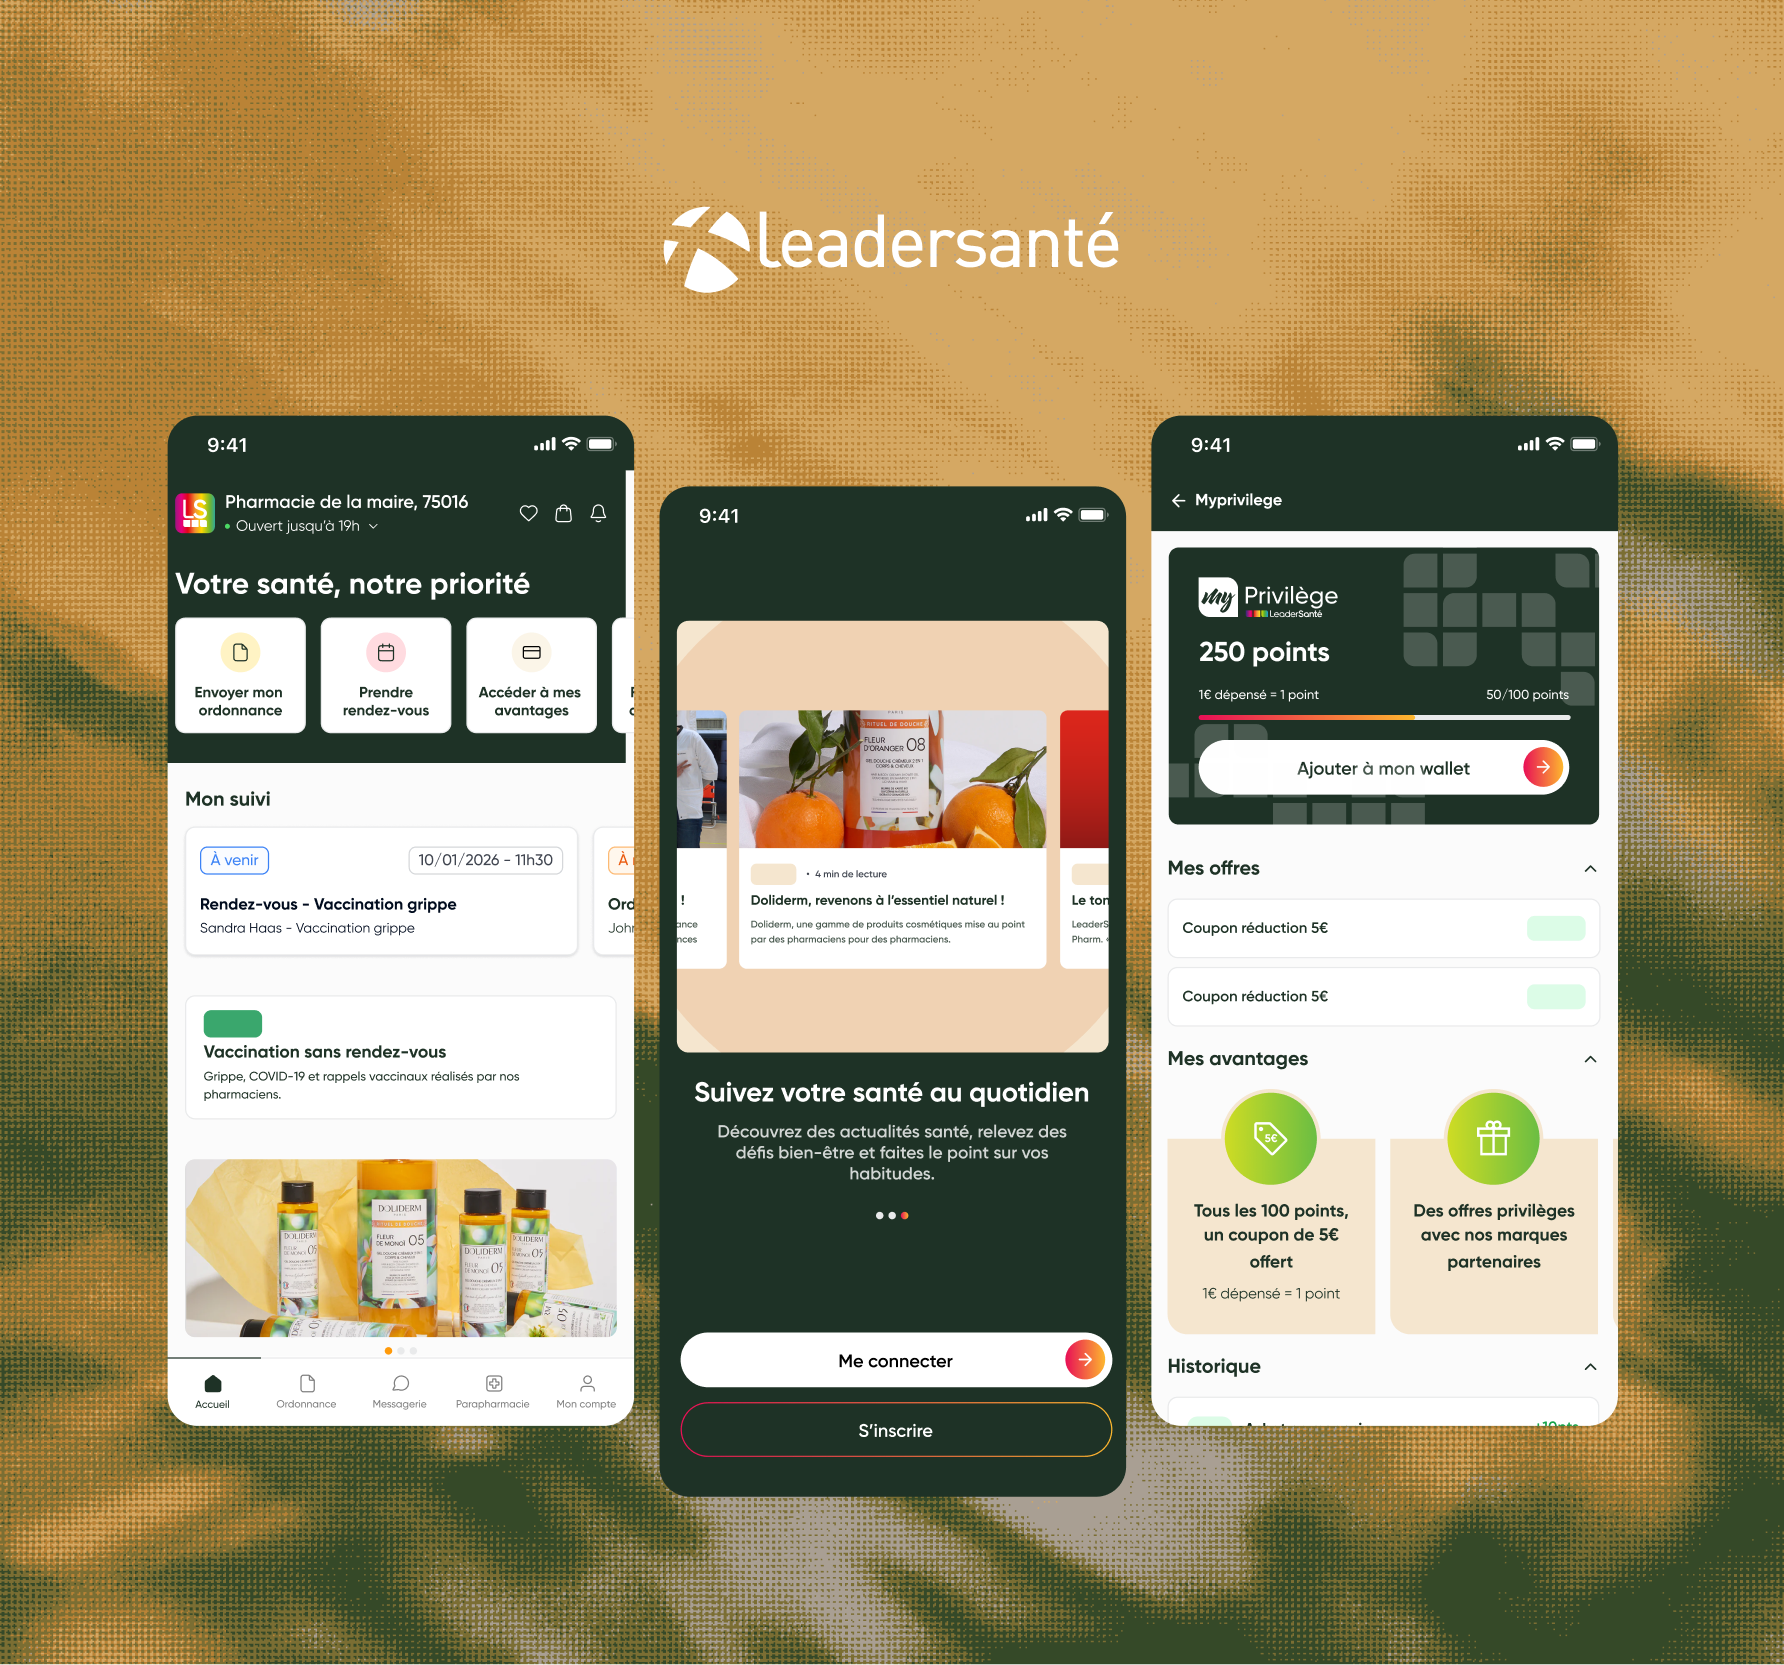
PharmacyLeadersanté

Centralising identities and access rights for a group of 900 pharmacies

Leadersanté's teams were working across some twenty business applications, each with its own login. Galadrim built the group's single sign-on portal: every satellite application connects to it, and identity and access management sits in one place. The whole ecosystem is hosted in an environment certified for health data.
900+pharmacies in the group
~20applications behind a single login
8 yearsof ongoing support
Leadersanté Logo
ObservabilityDatadog

Adding monitoring for a network security component to a US software vendor's integrations catalogue

Datadog, a monitoring and analytics platform for cloud infrastructure, wanted to bring metrics from Calico into its ecosystem. Calico is the open-source component that handles routing, network access control and security policy enforcement on Kubernetes containers. Galadrim developed the collection agent in Python, along with its test coverage, working in English directly with Datadog's teams. The code was then merged into Datadog's Core repository.
10k+users of the integration
$2.7bnrevenue in 2024
Datadog Logo
[Why Galadrim?]

Why work with our cybersecurity team?

Auditors who know how to fix

An audit firm stops at the report. Our auditors are software engineers: every flaw comes with an estimated time to fix, and our development teams carry out the remediation, then have it checked by a follow-up audit.
Strict separation of roles

Every application audit, including on applications Galadrim built, is carried out by engineers from outside the project. Every report is reviewed by a second auditor before it goes out.

The same security standards applied to our own work

Our repositories go through code reviews, automated detection of vulnerable dependencies and an internal audit programme. Our deliverables regularly pass the penetration tests our clients commission from third-party firms.
Hands-on security research

Our team carries out independent research, all the way to publishing previously unknown vulnerabilities and coordinating fixes with the vendors. We test your defences using the methods of offensive security research.

We help you secure your applications and infrastructure, from penetration testing to verified remediation.

Talk to an expert
[FAQ]

A few questions our clients often ask

It's your choice. With access to the code, the audit covers more ground in the same time. In black-box mode, the test reproduces the conditions of an outside attacker. We offer both on every engagement, and you decide during scoping.
A typical engagement combines a code audit and a penetration test over 5 to 10 days, depending on the number of applications and the depth of testing. We agree the scope with you before anything is signed.
An executive summary for your leadership, then each vulnerability described and rated using the CVSS standard, with proof of impact and an estimated time to fix. You also get a compliance roadmap aligned with ANSSI recommendations, and the risk model.
Yes. The audit is carried out by engineers from outside the project, and reports are reviewed by a second auditor. If your insurer or your client requires an auditor fully independent of our company, we'll tell you so openly and point you to the right partner.
Yes. We review the architecture and configuration of your AWS, Azure, GCP or OVH environments: identity management, network segmentation, storage, encryption, and hardening against the CIS Benchmarks.
Your teams or ours. We write the report so that any provider can work from it, and our engineers carry out the remediation if you ask us to.
We support the technical side of compliance, through regular audits and training for your teams. The certification itself is granted by an accredited body.
Confidentiality is the rule: we never name an audit engagement publicly, not even anonymously. You get the same discretion.
You do. Reports, proof of impact and documentation belong to you with every delivery. The transfer of rights is written into the contract from day one.
We size each engagement to your scope, your access method and the depth of testing you choose. Tell us about your context and we'll come back to you within 24 hours with an initial assessment.
[Contact us]

Let's bring your project to life together

We work with every kind of client, across every industry. Whether you are an entrepreneur or lead a large organisation, we put together a team that fits your need.

More than 800 companies have trusted us to build their web, mobile and AI products

Your request

We'll get back to you within the hour.